Confidential Virtual Machines
A confidential virtual machine (CVM) runs inside a hardware-enforced trusted execution environment on a host with AMD SEV-SNP or Intel TDX. NVIDIA Hopper and Blackwell GPUs that you pass through to the CVM extend that protection to GPU memory and to the data that moves between the CPU and the GPU.
The documentation for this product covers the following GPU modes:
- Confidential Computing (CC) mode with one GPU per CVM, on Hopper and Blackwell GPUs.
- CC mode with multiple GPUs per CVM, on Blackwell GPUs.
- Protected PCIe (PPCIe) mode with multiple GPUs per CVM, on Hopper GPUs.
Refer to Supported Platforms for the validated combinations of CPUs, GPUs, and operating systems. For trusted components, responsibilities, and protection limits, refer to Trust and Threat Model.
Workflow
The following figure shows the stages of deploying and using a CVM with confidential GPUs.
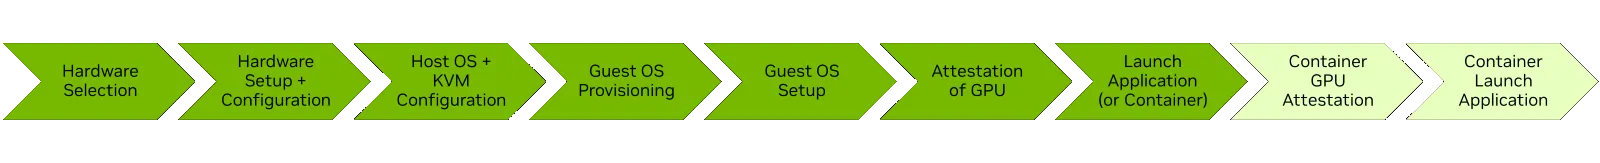
Different people can complete different stages. For example, a cloud service provider (CSP) can select and configure the hardware, configure the host, and provision the guest VM. A tenant of the CSP then sets up the guest OS, attests the GPU, and runs applications.
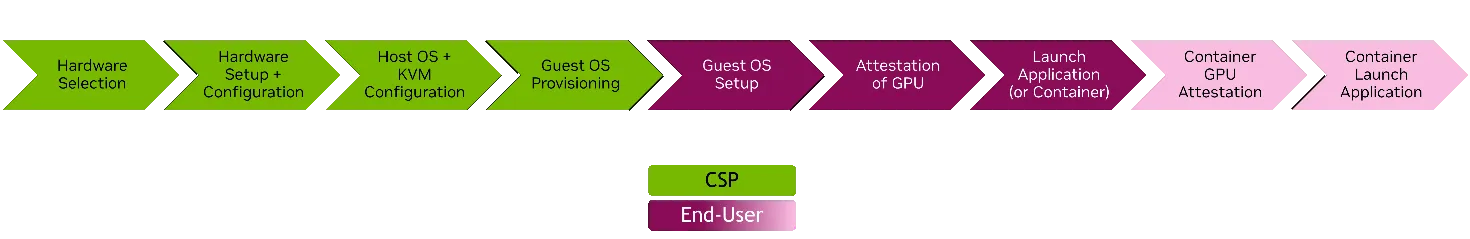
In this example, the CSP does not decide how often the tenant attests the GPU, and the tenant does not configure the GPU for confidential or non-confidential modes.
Personas
The Deployment Guide is organized by the following personas. Start with the section that matches your responsibilities, or read every section in order if you deploy the entire system.
Getting Help
To provide feedback or ask questions, use the NVIDIA Developer Forums for Confidential Computing.