

Isolation Backends
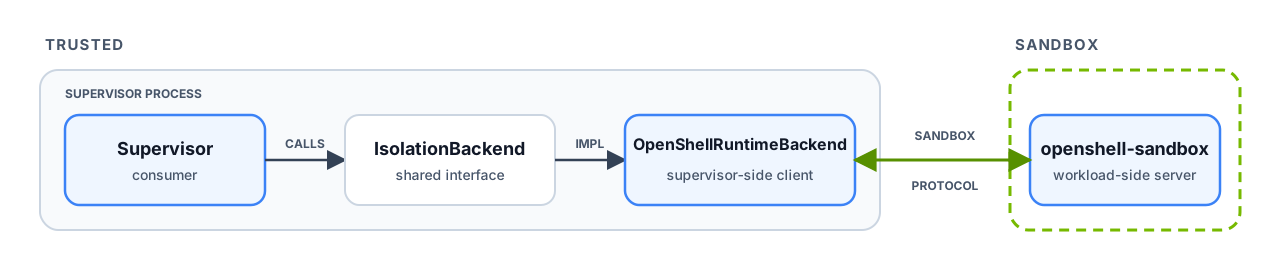
The supervisor uses the IsolationBackend RPC service to discover and bind an
isolation backend, then uses the Sandbox Protocol to launch and control the
agent workload. The built-in openshell-sandbox runtime and external backends
implement the same services, allowing different isolation mechanisms without
changing the gateway API or policy model.
The protocols
The services are defined in
isolation_backend.proto
and
sandbox_protocol.proto.
The supervisor’s concrete RPC client, OpenShellRuntimeBackend, lives in
openshell-sandbox-backend.
The admission sequence is Attach, Confirm, then StartAgent. No workload code runs before StartAgent.
External compute drivers advertise openshell.compute.isolation-backend to
accept an operator-selected IsolationBackendRegistration, including its Unix,
TCP, or vsock endpoint. The driver provisions the resource and delivers the
backend’s trusted launch metadata to the supervisor.
Who Owns What
For how openshell-sandbox enforces the boundary, refer to Inside the Sandbox
Boundary. For driver-specific
workload behavior, refer to Runtimes.