Skip to navigation

External Access to Critical Services

View as Markdown

NVIDIA Run:ai requires certain network connectivity and access. This page outlines the network endpoints and protocols that must be reachable from your NVIDIA Run:ai control plane and tenant cluster nodes to support installation, artifact retrieval, and ongoing platform communication.

Meeting these requirements ensures that:

  • Users and API clients can reach the NVIDIA Run:ai control plane and each tenant cluster
  • Tenant clusters can sync with and report metrics to the control plane
  • The control plane can reach the external metrics store
  • The control plane and tenant cluster nodes can pull the images required for installation
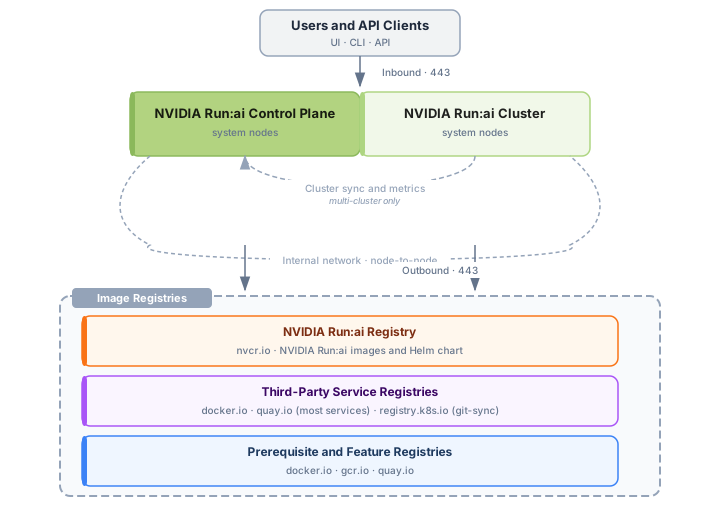
Network access map: inbound access from users and API clients, cluster sync and metrics between the control plane and each tenant cluster, internal node-to-node traffic, and outbound access to the NVIDIA Run:ai, third-party service, and prerequisite and feature image registries
CategoryRequirementDetails
InboundPorts open for user and API accessSee Inbound Rules
OutboundControl plane and tenant cluster syncSee Control Plane and Tenant Cluster Sync
OutboundMetrics store accessSee Metrics Store
OutboundNVIDIA Run:ai registry and catalog accessSee NVIDIA Run:ai Registry and Catalogs
OutboundNetworking component registry accessSee Networking Component Registries
OutboundThird-party service registry accessSee Third-Party Service Registries
OutboundPrerequisite and feature component registry accessSee Prerequisite and Feature Registries
InternalNode-to-node connectivitySee Internal Network

Note

Ensure the inbound and outbound rules below are correctly applied to your firewall before proceeding with installation.

Inbound Rules

To allow your organization’s NVIDIA Run:ai users to interact with the cluster using the NVIDIA Run:ai Command-line interface, or access specific UI features, certain inbound ports need to be open:

NameDescriptionSourceDestinationPort
NVIDIA Run:ai control planeHTTPS entry point0.0.0.0NVIDIA Run:ai system nodes443
NVIDIA Run:ai clusterHTTPS entry point0.0.0.0NVIDIA Run:ai system nodes443

Outbound Rules

Control Plane and Tenant Cluster Sync

NameDescriptionSourceDestinationPort
Cluster syncSync a tenant cluster with the NVIDIA Run:ai control planeTenant cluster system nodesNVIDIA Run:ai control plane FQDN443
Metric storePush tenant cluster metrics to the NVIDIA Run:ai control plane’s metric storeTenant cluster system nodesNVIDIA Run:ai control plane FQDN443

Metrics Store

The NVIDIA Run:ai control plane requires outbound access to the external metrics store configured for the deployment. See Metrics Store Requirements for the supported backends and their connection details.

NameDescriptionSourceDestinationPort
Metrics storeRead and write metrics to the configured external metrics storeNVIDIA Run:ai control plane system nodesGrafana Labs endpoint, or your Mimir instance’s FQDN443

NVIDIA Run:ai Registry and Catalogs

NameDescriptionSourceDestinationPort
NVIDIA Run:ai NGC RegistryPull NVIDIA Run:ai images and Helm chart for installationAll Kubernetes nodesnvcr.io443
NVIDIA NGCBrowse NGC catalogNVIDIA Run:ai control plane system nodesapi.ngc.nvidia.com443
Hugging FaceBrowse Hugging Face modelsNVIDIA Run:ai control plane system nodeshuggingface.co443

Networking Component Registries

The ingress controller you install as part of Networking Setup is pulled from the following registry:

NameDescriptionSourceDestinationPort
Ingress Controller RegistryHAProxy ingress controller image repositoryAll Kubernetes nodesdocker.io443

Third-Party Service Registries

NVIDIA Run:ai deploys the following third-party services as part of installation. Images are pulled from Docker Hub, Quay, or the Kubernetes registry. For the full list of services, see Third-Party Services.

NameDescriptionSourceDestinationPort
KeycloakIdentity federation and SSO serviceNVIDIA Run:ai control plane system nodesdocker.io / quay.io443
PostgreSQLCentralized platform databaseNVIDIA Run:ai control plane system nodesdocker.io / quay.io443
TraefikAPI gatewayNVIDIA Run:ai control plane system nodesdocker.io / quay.io443
NATSMessage brokerNVIDIA Run:ai control plane system nodesdocker.io / quay.io443
ValkeyWorkload cacheTenant cluster system nodesdocker.io / quay.io443
oauth2-proxyWorkload access authenticationTenant cluster system nodesdocker.io / quay.io443
git-syncGit data source syncTenant cluster system nodesregistry.k8s.io443

Prerequisite and Feature Registries

NVIDIA Run:ai requires additional prerequisite and feature components to be installed on each tenant cluster, such as the GPU Operator and Prometheus Operator. These components are pulled from the following registries:

NameTypeDescriptionSourceDestinationPort
NVIDIA NGC CatalogPrerequisiteGPU Operator image repositoryAll Kubernetes nodesnvcr.io443
Red Hat Container RegistryPrerequisitePrometheus Operator image repositoryAll Kubernetes nodesquay.io443
Google Container RegistryFeatureKnative image repositoryAll Kubernetes nodesgcr.io443
Docker Hub RegistryFeatureKubeflow Training Operator image repositoryAll Kubernetes nodesdocker.io443

Internal Network

Ensure that all Kubernetes nodes can communicate with each other across all necessary ports. Kubernetes assumes full interconnectivity between nodes, so you must configure your network to allow this seamless communication. Specific port requirements may vary depending on your network setup.

IPv6 Considerations

For IPv6-only environments, nvcr.io only has an IPv4 DNS record, so clients on IPv6-only networks cannot resolve it and image pulls will fail. Two options:

  • Configure NAT64/DNS64 - Translates between IPv6 and IPv4 so the cluster reaches the registry transparently.
  • Deploy an internal mirror registry - Use Harbor, Artifactory, or a similar registry over IPv6, configured to pull from nvcr.io over IPv4. Point the cluster at the mirror through the container runtime config and NVIDIA Run:ai Helm image-registry overrides.

gcr.io, quay.io, and docker.io are reachable over IPv6 directly.