

GitHub Actions
Bring skill evaluation to your GitHub repository with one workflow file. Choose your skill folders; pull requests check changed skills automatically. The shared image includes Tier 1 and SkillSpector security scanning.
Get started
Copy the ready-to-use template
Open skill-checks.yml
from the ready-to-use templates.
Use GitHub’s Raw view to copy it into .github/workflows/skill-checks.yml.
The template already supplies pinned workflow and image versions.
The released template provides checks and downloadable reports. Hosted reports and PR comments need the optional publisher setup. The same release also includes the optional publisher template.
I prefer to inspect the source templates
Browse the public template catalog
and skill-checks.yml source.
Source templates contain placeholders. Use the release-generated file when
onboarding; do not substitute main or latest for its immutable versions.
See what happened
Download skill-evaluator-tier1-attempt-N, extract it, and open index.html.
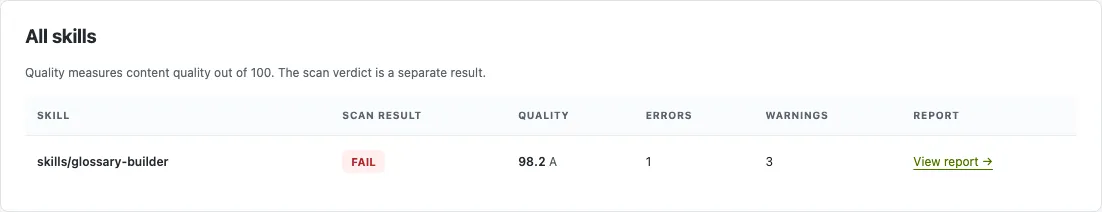
Failed scans retain their available reports too. The HTML separates the
verdict from the quality score: a high score does not override a failed
required security or schema check.
On the pull request
With publishing enabled, one bot comment is updated for new results. Reviewers see the issue and next step without reading the full Actions log.
github-actions[bot]
Tier 1 scan result: FAILED
1 skill · 0 passed · 1 failed · 0 incomplete
Problem: Quality score 98.2/100 is below the required 100/100.
Next step: Open the skill report and address its quality findings.
Open full report · View workflow run
Browse the public report and log examples for more detail. No personal demo-repository access is needed.
Enable PR comments
The optional publisher hosts the HTML and posts a comment after deployment succeeds. It needs a second workflow plus one-time hosting and approval settings.
Copy publish-skill-reports.yml from the same template folder as your scan workflow. Complete the one-time setup below, or let the CLI handle it.
What does manual publisher setup involve?
Start with the filled-in publisher template and follow the publisher setup guide. The main steps are:
- Enable Settings → Pages → Source: GitHub Actions and initialize the
gh-pagesreport-history branch. For private reports, an administrator must also select Private site visibility in GitHub’s settings; see the private-hosting requirements below. Preserve any existing site or history. - Add
publish-skill-reports.ymlwith your Pages URL. Keep the evaluator and publisher versions supplied by the release. - Grant the scan workflow
id-token: write, then approve its exact contents in the publisher’strusted-caller-blobsinput. Compute the value withgit hash-object .github/workflows/skill-checks.yml; refresh it whenever that scan file changes. - Merge both workflow files into the default branch. Open a new skill PR to test checks, hosting and feedback together.
Keep the Skill checks workflow name, scan filename and default artifact name. The publisher uses GitHub’s automatic token; organization policies must allow its permissions and referenced actions. Copying a second file alone does not finish setup.
Who receives a comment, and who can read the report?
Comments are posted on open, current-head PRs from branches in the same repository. Fork-origin PRs keep their available reports in Actions. Pages is public unless explicitly configured as private; repository privacy alone does not make its Pages site private. Reports may contain source excerpts and unmerged findings. Use downloadable artifacts when public hosting is unsuitable.
Can our private repository publish private reports?
Access-controlled Pages requires a private or internal project repository owned by a GitHub Enterprise Cloud organization. An administrator first selects GitHub Actions and Private in Settings → Pages. The REST API cannot set Pages visibility. Personal repositories cannot host private Pages.
The CLI verifies the existing private site and uses its assigned
*.pages.github.io URL. It accepts an existing SkillEvaluator report site
or a newly configured empty private site, and preserves unrelated websites.
If private hosting is unavailable, choose checks only. See
private report hosting for the
guided path and GitHub’s access-control requirements.
Fit it into your workflow
Will this wait for my existing workflows?
This workflow runs independently. Existing workflows remain separate; it does not automatically wait for them to finish. Configure explicit workflow dependencies if your pipeline needs that ordering.
Which changes trigger a scan?
auto selects affected skills on pull requests. Pushes to the default
branch and manual runs scan the configured collection. all scans that
collection each time. No changed skills is a successful Skipped result,
not a scanner pass. Changes to shared files outside the skill roots are not
inferred dependencies; use all when they should trigger a full scan.
Selection is capped at 100 skills. Timeouts retain completed results and
mark unfinished work incomplete. The workflow scans up to four skills at
once; scan-workers accepts 1–16.
How do I make this a merge gate?
After the first run, select its scan check in GitHub branch rules. The
current template emits skills / Tier 1 scan; use the actual check name
shown in your repository. min-score sets the quality threshold; required
security, schema and other checks remain independent. This integration
runs Tier 1 only.
The scan finished, but the comment is missing
Confirm setup is on the default branch and the PR is eligible for comments.
Open Publish skill reports to see whether deployment completed. If
hosting was skipped, check the scan’s id-token: write permission and
trusted-caller-blobs value. A new scan must use the updated workflow;
rerunning an old job keeps its original workflow. The scan’s downloadable
report remains a separate way to inspect available findings.
Do the checks need an LLM key or network access?
Default Tier 1 checks use no model key. Dependency audits can contact vulnerability services and submit package metadata; packages are not installed and build scripts are not run. Optional LLM checks use a separate manual workflow, your provider key and provider charges. They send selected content to that provider and are outside the default publisher allowlist.