

Container Registries
When a user creates a new container, an image specified by the user should be used. The images are kept either locally on a host, or in a registry. The image registry can be provided by a cloud provider or locally.
3.1 Container Registries: Introduction
3.1.1 Docker Hub, A Remote Registry
By default, Docker searches for images in Docker Hub, which is a cloud-hosted public and private image registry. Docker Hub serves a huge collection of existing images that users can make use of. Every user is allowed to create a new account, and to upload and share images with other users. Using the Docker client, a user can search for already-published images, and then pull them down to a host in order to build containers from them.
When an image is found in the registry, the Docker client verifies if the latest version of the image has already been downloaded. If not, then it downloads the images, and stores them locally. It also tries to synchronize them when a new container is created.
Docker Hub maintains limits for the number of requests. To help get around the issues caused by the limits:
-
A personal account can be created on Docker Hub, and the credentials used for pulls. Authenticated requests for personal accounts have a greater pull rate allowance than unauthenticated requests.
-
A Pro, Team, or Business account (https://docs.docker.com/docker-hub/usage/pulls/) can be created on Docker Hub, and the credentials used for pulls. Authenticated requests for these accounts have an unlimited pull rate allowance.
-
For a connected cluster, configuring a Docker Registry as a caching proxy mirror for Docker Hub (section 3.2.1) reduces the number of Docker Hub GET requests.
-
Using Skopeo to manage container images and repositories helps minimize pulls for air-gapped clusters (Appendix C).
3.1.2 Local Image Registry Options: Classic Docker Registry Vs Harbor
Besides using Docker Hub for the image registry, the administrator can also install a local image registry on the cluster. BCM provides two ways to integrate such a local registry with the cluster, based on existing open source projects:
-
The first one is the classic Docker registry originally provided by Docker Inc, and can be useful if the registry is used by trusted users, or when a Docker Hub proxy cache is required. Maintenance has been handed over to the CNCF, and future releases will be named CNCF Distribution.
-
The second registry, Harbor, provides additional features such as security and identity management, and is aimed at the enterprise.
Both options can be installed with the cm-container-registry-setup utility, which comes with BCM’s cm-setup package.
3.2 Container Registries: Setup And Configuration
Docker Registry and Harbor can be installed using the cm-container-registry-setup TUI utility, which comes with the cm-setup package.
They can also be installed using Base View as follows:
-
The Container Registry Deployment Wizard is launched via the Base View navigation path:
Containers>Container Registry Wizard -
Either Docker Registry, or Harbor, should be chosen as a registry.
-
A single node is ticked for the deployment. The address, port, and the root directory for storing the container images are configured. If the head node is selected for Harbor, then the setup later on asks to open the related port on the head node. This is to make Harbor and the Harbor UI externally accessible.
-
In the summary page, if the
Ready for deploymentbox is ticked, then the administrator can go ahead with deploying the registry. -
When the deployment is complete, the Docker Registry becomes ready for use. Harbor can take a few additional minutes to be ready for use.
Similar to the case of etcd nodes (section 4.2), nodes that run Harbor or Docker Registry have the datanode option (here) when installed by BCM utilities. The option helps prevent the registry being wiped out by accident, and is added when the cm-container-registry-setup utility is used to install Harbor or Docker Registry. This extra protection is put into place because if a registry is wiped out, then the state of images in the container becomes incoherent and cannot be restored.
3.2.1 Docker Registry As A Pull Through Cache For Docker Hub
Docker Hub has a pull rate limit since November 2020 to limit the number of images that can be pulled per hour (https://docs.docker.com/docker-hub/usage/). To limit the number of direct requests to Docker Hub, Docker Registry can be configured as a caching proxy mirror for Docker Hub.
When configured as a proxy mirror, Docker Registry serves cached images from Docker Hub, and downloads content from Docker Hub only when required.
Docker Registry is configured for proxy mode by selection during a cm-container-registry-setup run (figure 3.1):

Figure 3.1: cm-container-registry-setup: configure Docker Registry as proxy cache
To access the proxy mirror, the port must be specified with the URL. For example, if Docker Registry is installed on node001 using the default port, (5000) with cm-kubernetes-setup, then it is specified for Kubernetes as https://node001:5000 (figure 3.2):
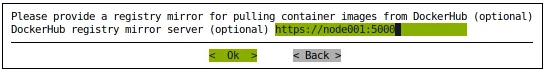
Figure 3.2: cm-kubernetes-setup: configuring a local proxy mirror
For example, if a Docker Registry proxy cache is configured on node001, port 5000, then the hello-world image is pulled explicitly through the proxy with:
Example
3.2.2 Harbor UI
If the head node is where Harbor is to be installed, and is to be made externally accessible, then the Harbor UI can be accessed at https:// <head node hostname>:9443.
If a different node is used for Harbor to be installed, then the related port must be forwarded locally.
Harbor can be logged into by default with the admin user and the default Harbor12345 password.
It is recommended to change that password after the first login.
3.2.3 Docker Registry And Harbor Configuration
Configuration is carried out using generic roles, which are roles with the prefix generic::, and that follow a generic template used by many roles.
-
Generic Docker Registry configuration is managed with the
generic::docker-registryrole. Thedocker-registrydaemon is documented upstream at https://github.com/docker/distribution. -
Generic Harbor configuration is managed with the
generic::harborrole. The Harbor registry is documented upstream at https://goharbor.io.
Inspecting the options in the roles for Docker and Harbor shows what can be managed.